
ISO 27001 Certification: Strengthening Information Security
Contents |
[edit] Introduction
Organisations increasingly depend on digital systems, cloud platforms, networks and electronic information to conduct their activities. Protecting this information requires more than technical security measures; organisations also need structured processes for identifying risks, implementing controls, responding to incidents and continually improving their security arrangements. ISO/IEC 27001 provides requirements for establishing, implementing, maintaining and continually improving an Information Security Management System (ISMS).
[edit] What is ISO 27001 certification?
ISO/IEC 27001:2022 is an international standard that specifies requirements for an Information Security Management System. It takes a risk-based approach to information security and addresses the protection of information in terms of confidentiality, integrity and availability.
An organisation can implement an ISMS in accordance with ISO/IEC 27001 without obtaining certification. Certification involves an independent certification body assessing the organisation's ISMS against the requirements of the standard and, where the requirements are met, issuing a certificate covering a defined scope.
The ISMS can be applied to an organisation as a whole or to a defined part of its activities, depending on the scope established by the organisation. The scope, organisational context, information assets, processes and identified risks determine how the ISMS is designed and which controls are necessary.
ISO/IEC 27001:2022 was published in October 2022 and replaced the 2013 edition. Amendment 1:2024 introduced climate-change considerations into clauses 4.1 and 4.2, requiring organisations to determine whether climate change is a relevant issue and recognising that relevant interested parties may have requirements relating to climate change.
[edit] Key elements of an ISO 27001 information security management system
[edit] Information security risk assessment and treatment
Organisations identify information security risks associated with their information assets, systems, processes, suppliers and other relevant activities. Risks are assessed against defined criteria and treated according to the organisation's risk acceptance and treatment approach. Risk treatment can involve implementing controls, avoiding an activity, transferring risk or accepting a residual risk.
ISO/IEC 27001:2022 does not require organisations simply to adopt every control listed in Annex A. Necessary controls are determined through the organisation's risk treatment process and other requirements. Annex A provides a reference set of controls against which the organisation can compare its risk treatment arrangements and establish whether any relevant controls have been omitted. The organisation documents its decisions in a Statement of Applicability.
[edit] Policies, responsibilities and competence
The ISMS establishes information security policies, responsibilities and processes appropriate to the organisation. Management has defined responsibilities under the standard, while personnel whose work affects information security need appropriate competence and awareness.
Policies and procedures can address areas such as information classification, acceptable use, access management, asset management, supplier relationships, information transfer and incident response.
[edit] Security controls
ISO/IEC 27001:2022 contains a reference set of 93 information security controls in Annex A. These are grouped into four categories: organisational, people, physical and technological controls. ISO/IEC 27002:2022 provides guidance on implementing information security controls.
The controls selected or developed by an organisation should reflect its information security risks, business requirements and applicable legal, regulatory and contractual obligations. Controls can include access control, authentication, cryptography, physical security, malware protection, backup, logging, monitoring, vulnerability management and supplier security.
[edit] Incident management
An ISMS includes processes for identifying, reporting, assessing and responding to information security incidents. Incident management can include containment, investigation, recovery, communication and the recording of lessons learned. Information from incidents and near misses can be used to improve risk assessments and security controls.
[edit] Business continuity and resilience
Information security arrangements can support business continuity by addressing the availability and resilience of information and information-processing facilities. Organisations can establish appropriate arrangements for backup, recovery, redundancy and continuity according to their identified risks and business requirements.
Business continuity is related to, but distinct from, information security. ISO/IEC 27001 does not replace dedicated business continuity management arrangements where these are required.
[edit] Monitoring, audit and continual improvement
The performance of an ISMS is monitored and evaluated using appropriate measures and other forms of evidence. Internal audits provide a systematic means of assessing whether the ISMS conforms to the organisation's own requirements and to ISO/IEC 27001.
Management reviews, corrective actions, risk reassessment and other improvement activities support the continual improvement of the ISMS. Certification assessments by an independent certification body provide an external assessment of conformity within the defined certification scope.
[edit] Benefits and application of ISO 27001 certification
Implementing an ISMS in accordance with ISO/IEC 27001 can help organisations to:
- establish a structured approach to information security;
- identify, assess and treat information security risks;
- clarify information security responsibilities;
- improve information security policies and procedures;
- strengthen controls over information and information-processing facilities;
- increase awareness and competence in relation to information security;
- support incident preparedness and organisational resilience;
- provide evidence of a systematic approach to information security management; and
- establish processes for monitoring and continual improvement.
ISO/IEC 27001 can be applied to organisations of different sizes and types, including organisations in technology, professional services, finance, healthcare, education, manufacturing, construction, logistics and other sectors. It is particularly relevant where organisations manage sensitive, confidential or business-critical information, or where information security requirements form part of customer, supplier, regulatory or contractual relationships.
Certification does not provide an absolute guarantee that an organisation will prevent data breaches, cyber attacks or other information security incidents. It provides independent assurance that the defined ISMS has been assessed against the requirements of the standard at the time of certification and within the stated scope.
[edit] Preparing for ISO 27001 certification
An organisation preparing for certification will normally first establish the scope and context of its ISMS and identify relevant interested parties, requirements and information security risks. A gap assessment can then be used to compare existing arrangements with the requirements of ISO/IEC 27001 and identify areas requiring further development.
The organisation can subsequently establish its information security policy and objectives, conduct risk assessments, determine and implement appropriate risk treatments and controls, allocate responsibilities, provide appropriate competence and awareness, and establish processes for monitoring and managing information security.
Before certification, the organisation needs to operate the ISMS and generate appropriate evidence that its processes and controls are functioning as intended. Internal audits and management reviews are important parts of this process and can identify nonconformities and opportunities for improvement.
Certification is carried out by an independent certification body. The assessment normally includes an initial review of the management system documentation and arrangements, followed by a more detailed assessment of the implementation and effectiveness of the ISMS. Continued certification is subject to ongoing surveillance and periodic reassessment in accordance with the certification body's certification scheme.
[edit] Related articles on Designing Buildings
Featured articles
Check out some of the best features and news from Designing Buildings as well as key stories from around the web.
Undervaluing our industrial past
Heritage value changes as taste for building styles changes.
Changing expectations around competence and compliance
New information sheet from CIAT.
Grenfell investigation files passed to CPS
Angela Rayner apologises on behalf of the British state.
Electrical contractors need to understand the practical implications.
The real barrier to getting more value from digital technology.
Your guide to The Construction Reset at UKCW Birmingham.
Accommodating the Victorian and Edwardian working woman. Book review.
Rethinking passive fire protection in design
PFP demands the same level of design rigour as structure or services.
38% of Gen Zs feel safe when a fire door is wedged open.
Stunning images from around the world
Shortlist for CIOB’s Art of Building photography competition.
Guidance for conversion of traditional pre-1919 stone buildings.
Industrial heritage in the Ruhr
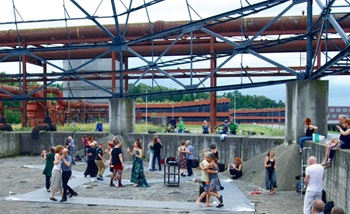
A marked difference to the fate of industrial landscapes in the UK.